AI Voice Agent Security: Risks, Compliance & Best Practices
Learn how to secure AI voice agents, manage compliance risks, and protect customer data. Explore GDPR, HIPAA, SOC 2, AI security threats, and more.
 Ranya Kharbach
- Deploying an AI voice agent means handling customer identities, phone numbers, conversations, and sometimes payment or health data, so security needs to be considered from planning through ongoing operation, not added later.
- Compliance and security aren't the same thing. Compliance is meeting a legal or regulatory bar; security is the technical and organizational work that gets you there, and keeps working after the audit.
- Key features to evaluate include: encryption, role-based access control (RBAC), multi-factor authentication (MFA), audit logs, API security, data retention controls, and monitoring.
- Which standards matter depends on your business: HIPAA for healthcare, GDPR for EU customers, SOC 2 or ISO 27001 for enterprise procurement.
- AI systems carry risks that legacy phone systems never had to think about: prompt injection, hallucinations, prompt leakage, and voice spoofing among them.
- Ask vendors directly: where is data stored, how long is it retained, is RBAC supported, and can customer data actually be deleted on request?
A healthcare provider wants to automate appointment scheduling calls. Before a single call goes live, they need answers to a specific set of questions: how is patient data protected in transit and at rest, how are callers authenticated before any account-specific detail is shared, is there an audit trail for every interaction, and does the platform actually support the HIPAA obligations that come with handling protected health information? Skipping any one of these isn't a minor oversight. It's a compliance gap that surfaces at the worst possible time, usually during an audit or after an incident.
That's the reality of implementing an AI voice agent in any business handling sensitive information. Automation is the visible part. Security and compliance are the parts that determine whether the automation is actually safe to run.
Why Security Matters for AI Voice Agents
An AI voice agent touches more sensitive information than it might first appear. Over the course of a single call, it can process a caller's identity, phone number, the full conversation itself, potentially payment details, and whatever gets sent back to a CRM record.
A simplified view of where that information flows:
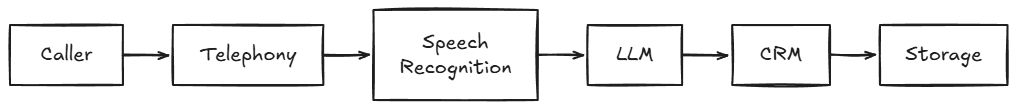
Every one of those steps is a place where sensitive data is either transmitted, processed, or stored. The more business-critical the workflow — for eg., booking a medical appointment rather than answering a general product question — the stronger the security requirements need to be around every stage of that flow.
Understanding AI Voice Agent Compliance
A distinction worth being precise about: compliance and security are related, but they're not interchangeable, and treating them as the same thing is a common buyer mistake.
- Security is the technical and organizational work: encryption, access controls, monitoring, incident response.
- Compliance is meeting a specific legal, regulatory, or contractual requirement, which usually depends on strong security, but also depends on policies, documentation, and processes that go beyond the technology itself.
A useful way to think about how they connect:
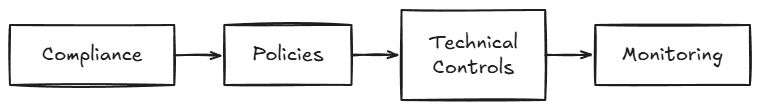
You can have strong security without being compliant with a specific regulation you haven't formally addressed. You generally can't be compliant without solid underlying security.
Key Security Features to Evaluate
Capability | Why It Matters |
|---|---|
Encryption | Protects data in transit and at rest |
RBAC | Limits access to only what each user's role requires |
MFA | Reduces the risk of unauthorised account access |
Audit Logs | Supports investigations and demonstrates compliance |
API Security | Protects the integrations connecting the AI to other systems |
Data Retention Controls | Meets regulatory requirements around how long data is kept |
Monitoring | Detects suspicious or anomalous activity as it happens |
Important Compliance Standards
A brief, non-legal overview of when each standard becomes relevant, since this varies significantly by industry and customer base:
- GDPR is the EU's data protection regulation. It applies the moment you're processing personal data belonging to anyone in the EU, no matter where your company is headquartered.
- SOC 2 is an AICPA audit framework, and it's what enterprise buyers commonly ask for before they'll even sign a contract. It's built around five trust categories, security, availability, processing integrity, confidentiality, and privacy. Every SOC 2 report includes the Security Trust Services Criteria, while the remaining criteria are optional depending on scope.
- ISO 27001 is the international standard for information security management, jointly published by ISO and IEC. It comes up constantly in enterprise procurement outside the US, sometimes alongside SOC 2, sometimes instead of it.
- HIPAA is the US federal law covering protected health information, enforced through a Privacy Rule and Security Rule that HHS administers. If a vendor processes health data at all, they need a signed business associate agreement, not just a vague assurance that they take privacy seriously.
- PCI DSS is the global payment card standard, run by the PCI Security Standards Council. It applies to anyone storing, processing, or transmitting cardholder data.
None of this is legal advice, and multiple standards frequently apply simultaneously. A healthcare provider serving EU patients through an enterprise procurement process is realistically looking at HIPAA, GDPR, and SOC 2 all at once.
Worth noting here: several AI voice platforms, telli included, are built around meeting multiple of these standards simultaneously rather than treating them as separate boxes to check later. telli is GDPR, SOC 2, and HIPAA compliant, and hosts the LLMs serving customer conversations on EU-based infrastructure specifically to support these requirements. That kind of infrastructure decision, not just a compliance badge on a pricing page, is usually a better signal of how seriously a vendor takes compliance than the certification list alone.
AI-Specific Security Risks
This is where AI voice agents introduce risks a legacy phone system never had to account for:
Prompt Injection
Business Impact: A caller tricks the model into revealing private information or behaving outside of its expected parameters. Can be used to exfiltrate data.
Mitigation: Strict input validation and monitoring of calls for injection attempts.
Hallucinations
Business Impact: The model appears to provide accurate information, but in reality, it is inventing information, potentially leading to customer harm or legal liability.
Mitigation: Configuring the agent to answer only when supported by approved knowledge sources, with fallback responses when it cannot provide a reliable answer.
Prompt Leakage
Business Impact: A caller is able to discover information about the model’s internal workings by asking the right questions.
Mitigation: Configuring the model not to reveal any information about itself and testing it against common injection attempts.
Sensitive Data Exposure
Business Impact: A caller inadvertently or intentionally discovers private information about another customer.
Mitigation: Never sharing information about other customers, even if it appears that they have requested it.
Model Abuse
Business Impact: The model is used for purposes outside of its intended scope, such as spamming or scams.
Mitigation: Monitoring for and preventing such abuse at the platform level.
Social Engineering
Business Impact: An attacker pretends to be another customer in order to gain information or perform an action they are not authorized to take.
Mitigation: Authenticating calls before sharing or acting on any information that requires authorization.
Voice Spoofing
Business Impact: An attacker fakes a customer’s voice in order to impersonate them.
Mitigation: Not authenticating based on voice alone for sensitive operations.
Securing Knowledge Bases & Integrations
The AI itself isn't the only thing that needs securing. Everything it's connected to, knowledge bases, CRMs, calendars, internal tools, needs the same level of scrutiny, because a well-secured AI agent connected to a poorly secured CRM integration is still a real vulnerability.
The architecture worth thinking through:
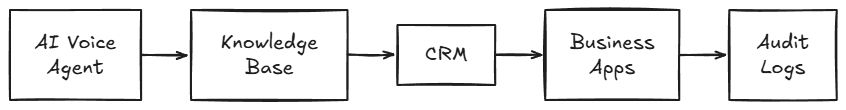
Apply least-privilege access throughout: the AI should only be able to read or write exactly what a given workflow requires, not have broad access to every field in a CRM just because the integration was easiest to set up that way.
Governance & Access Controls
As a deployment scales past a small pilot, governance becomes as important as any individual technical control. Worth having in place:
- Admin roles that clearly separate who can view analytics, who can edit prompts, and who can manage integrations
- Prompt approval workflows so changes go through review before reaching live callers, not straight from someone's edit to production
- Version control for prompts, with the ability to roll back a change that performs worse than expected
- Change management documentation, so there's a clear record of what changed, when, and why
- Audit history covering both calls and configuration changes
- User permissions reviewed periodically, not just set once at implementation and forgotten
Questions Every Buyer Should Ask Vendors
When purchasing an AI voice agent, it is important to ask the following questions in writing, rather than assuming that a vendor’s public claims represent everything they are capable of:
- Where is customer information stored? Does this affect your ability to comply with any regulations?
- How long are conversations retained, and can this be configured?
- Are transcripts and recordings encrypted?
- Is role-based access control supported?
- Which compliance standards do you support? Can you provide the documentation to prove it?
- How are prompts managed, and is there an approval workflow before changes take effect?
- Can customer data be deleted, and if so, how quickly?
- If call recording is necessary to comply with a regulation, how is consent obtained? Some platforms, including telli, have built-in support for obtaining verbal consent from a caller before recording begins.
Common Security Mistakes
Overprivileged Accounts
Business Impact: An account is compromised and is able to access or modify more information than a user should be allowed to.
Recommendation: Only grant access to the information that a given user needs in order to perform their job.
Unencrypted Connections
Business Impact: Information sent between the AI voice agent and connected systems is intercepted by unauthorized parties.
Recommendation: Ensure that all connections are encrypted.
Weak Authentication
Business Impact: Compromise of an account due to weak credentials being too easy to guess.
Recommendation: Requiring multifactor authentication for account access and prompt editing.
Lack of Logging
Business Impact: Unable to investigate a security incident due to insufficient or nonexistent logging.
Recommendation: Design logging and auditing into the deployment, rather than attempting to retrofit it later.
No Governance
Business Impact: Prompts and permissions are changed without oversight, potentially introducing security issues.
Recommendation: Set up basic governance procedures before launching the voice agent.
Poor Vendor Evaluation
Business Impact: Assuming that a vendor offers sufficient security when, in reality, their public claims are misleading.
Recommendation: Ask vendors for documentation rather than relying on third-party assurances.
Enterprise Security Checklist
Identity
- MFA enforced for all administrative access
- Role-based access control configured and reviewed regularly
Data
- Encryption in transit and at rest confirmed
- Data retention periods defined and configurable
- Clear process for data deletion requests
Infrastructure
- Data residency confirmed against your specific regulatory requirements
- API security reviewed for every integration point
AI
- Prompt injection safeguards tested
- Grounding and fallback behavior confirmed to reduce hallucination risk
- Sensitive data isolation verified across customer records
Governance
- Admin roles and permissions clearly defined
- Prompt approval and version control process in place
Compliance
- Relevant certifications (SOC 2, ISO 27001, HIPAA, GDPR) confirmed in writing
- Business associate agreement in place if handling health information
Monitoring
- Real-time monitoring for anomalous activity
- Audit logs covering both calls and configuration changes
Incident Response
- Documented incident response plan, tested rather than theoretical
- Clear breach notification timeline defined in the vendor agreement
Where This Leaves You
Strong AI voice agent security isn't achieved by checking off a single compliance standard and moving on. It requires secure architecture from the start, ongoing governance as the deployment scales, ongoing monitoring, and continuous risk management rather than a one-time review. Businesses evaluating AI voice agent platforms should weigh security and compliance alongside AI capabilities, integrations, and analytics, not as an afterthought once the rest of the decision is already made.
If you’re considering how to go about implementing AI voice agents the right way, book a call with one of telli’s automation experts.
Sources used
- commission.europa.eu - Official GDPR legal framework, European Commission
- aicpa-cima.com - SOC 2 Trust Services Criteria, AICPA
- iso.org - ISO/IEC 27001 official standard page
- hhs.gov - HIPAA Privacy Rule summary, U.S. Department of Health and Human Services
- pcisecuritystandards.org - PCI DSS official standard, PCI Security Standards Council
- telli.com - telli's GDPR, SOC 2, and HIPAA compliance posture, EU-hosted infrastructure, and call recording consent flow
Frequently Asked Questions
It depends entirely on the specific platform and how it's configured, there's no universal answer. Evaluate encryption, access controls, audit logging, and the vendor's actual compliance documentation rather than assuming security by default.
It depends on your industry and customer base: GDPR for EU customers, HIPAA for health information, SOC 2 or ISO 27001 for enterprise procurement, and PCI DSS if payment data is involved.
Yes, if any of your callers are in the EU, regardless of where your business is headquartered. GDPR applies based on whose data is being processed, not where the vendor operates.
Yes, with the right safeguards in place, encryption, access controls, and appropriate compliance certifications for your industry. Without those safeguards, handling sensitive data through any AI system carries real risk.
Across technical controls (encryption, RBAC, MFA, monitoring), compliance certifications relevant to your industry, and governance processes (prompt approval, audit history, access reviews), rather than any single factor in isolation.
Where data is stored, how long it's retained, whether transcripts are encrypted, which certifications the vendor actually holds (with documentation, not just a claim), and how quickly customer data can be deleted on request.
Maybe you’re also interested in
AI for Customer Engagement: Proven Strategies, Tools & Best Practices
Unlock higher retention with AI: Explore actionable strategies, real-world results, and top tools for AI-powered customer engagement.
Read nowAI Lead Qualification: How Voice Agents Qualify Leads Faster
Learn how AI voice agents qualify leads instantly, capture key data, and increase conversions with faster, more consistent follow-up.
Read nowWe Break Down the Best AI Voice Agents For Appointment Booking
AI voice agents are on the rise, but which ones truly deliver bookings? We explore the top options and what sets them apart.
Read nowChurn Rate: How To Measure, Benchmark, And Reduce Customer And Employee Churn
A practical guide to understanding both customer and employee churn, the benchmarks that matter, and how AI voice agents can reduce attrition across the board.
Read now